
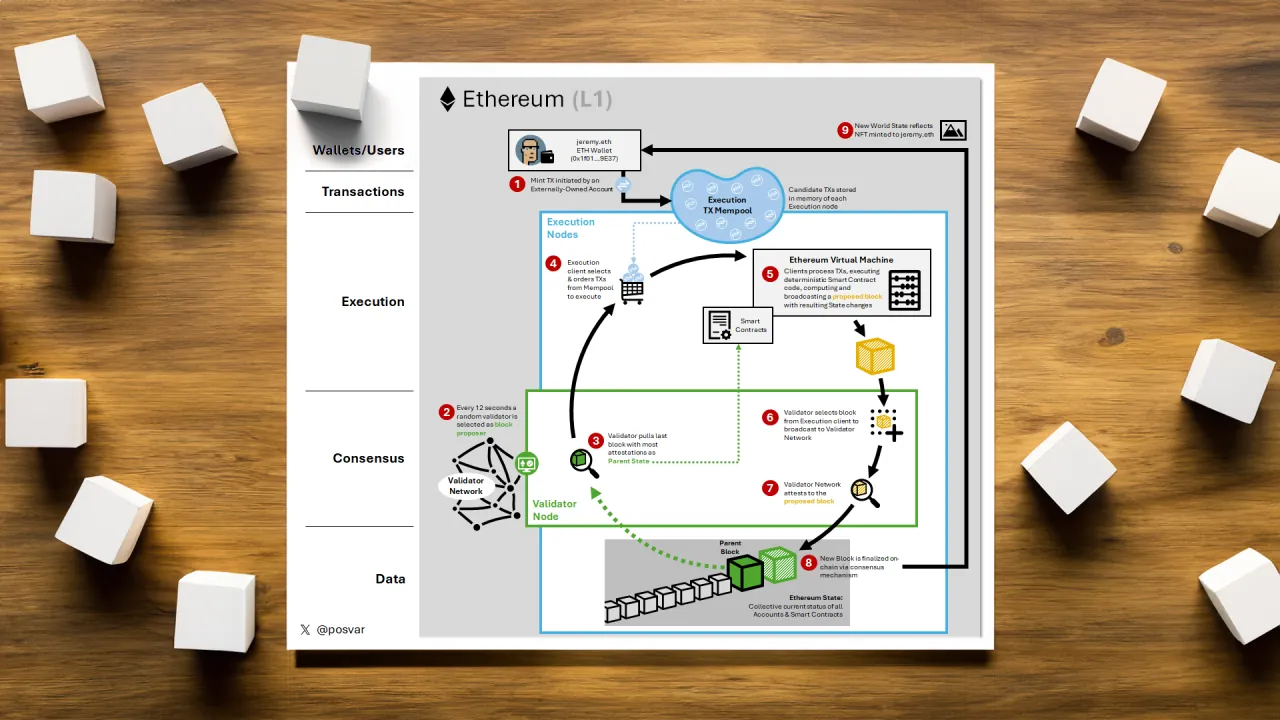
The notorious Maximal Extractable Value bot known as Jaredfromsubway.eth has been exploited for $7.5 million. The incident occurs amid escalating on-chain warfare, where white-hat hackers and automated agents constantly probe the MEV-Boost ecosystem for reentrancy vulnerabilities and misconfigured relays.
Between November 2024 and October 2025, this specific bot dominated the decentralized finance space. The automated agent executed approximately 70% of all sandwich attacks on the Ethereum network, according to Cointelegraph.
While initial reports peg the loss at $7.5 million, conflicting data from SolanaFloor suggests the true scale of the exploit could reach $17 million. The discrepancy creates immediate anxiety regarding the security of EVM-compatible trading bots across the broader market.
Named mockingly after the disgraced former fast-food spokesman, the bot became infamous for its ruthless efficiency. It monitors the public mempool for pending decentralized exchange trades and “sandwiches” them. It executes a buy order right before the victim and a sell order right after, pocketing the artificially inflated spread. At its peak, the bot extracted over $34 million in revenue, once draining a user of $215,000 in a single stablecoin swap.
How the Exploit Impacts EVM Searchers and Retail Traders
The exploit sends a direct shockwave through the automated decentralized finance community. Rival MEV bot operators and searchers who rely on similar smart contract architecture are now forced to audit their code for matching vulnerabilities. For retail traders, who have collectively lost tens of millions of dollars to the bot’s predatory slippage tactics over the last two years, the exploit brings mixed reactions as one of the network’s most aggressive extractors is sidelined.