
Managing a self-hosted home lab tunnel is satisfying right up until it breaks while you are sitting in a hotel room 500 miles away. That exact scenario prompted XDA Developers reviewer Joe Rice-Jones to rip out his hand-written WireGuard configuration and deploy NetBird instead. Raw WireGuard offers incredible cryptography and blinding speed. But when a connection drops, its reliance on a basic command-line interface leaves remote users virtually blind.
NetBird solves this operational headache without sacrificing underlying security. It maintains the exact same WireGuard architecture underneath, but layers a powerful, visually intuitive control plane in front of it. You no longer have to guess why a peer is offline or comb through terminal logs just to access your own files.
What We Know
- Core Architecture: NetBird operates as a Zero Trust network security platform, utilizing kernel-mode WireGuard to encrypt traffic directly between peers.
- Simplified Routing: Users can monitor every connected peer instantly and utilize built-in reverse proxy capabilities to manage public service exposure.
- Traffic Passthrough: The switch allowed Rice-Jones to route TLS traffic through tools like Traefik without the frustration of manual SSL certificate renewals.
- Developer Adoption: The platform encourages engineers to stress-test the mesh network in their personal homelabs before proposing corporate enterprise integrations.
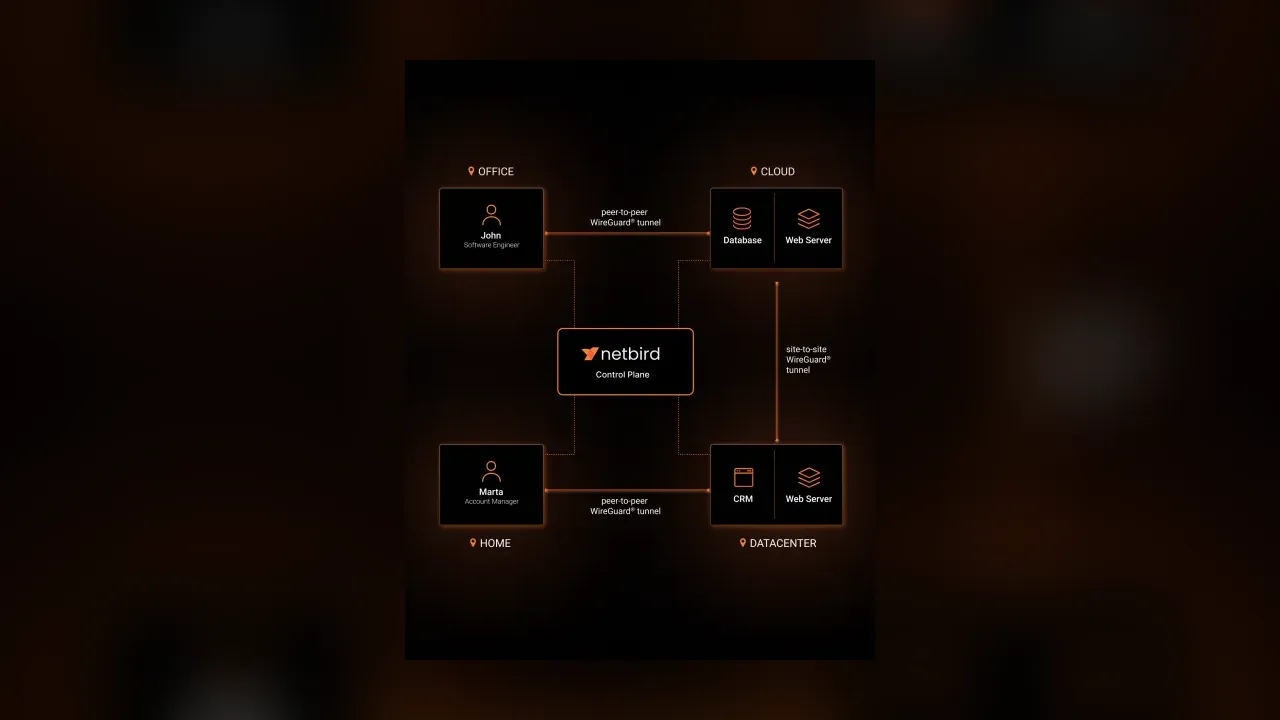
Instead of manually assigning IP addresses and generating public keys for every new device, NetBird handles the orchestration automatically. The software creates a true peer-to-peer mesh. This means your phone talks directly to your home server, rather than bouncing traffic off a centralized cloud server that slows down your connection.
The tech industry is backing this architectural shift with serious capital. Founded in Berlin in 2021 by Misha Bragin and Maycon Santos, the platform is rapidly scaling beyond individual home networks. Earlier this year, the company secured a generous $10 million Series A funding round led by Pace Capital to aggressively expand its open-source networking ecosystem.
That funding is fueling a direct assault on the enterprise networking market. NetBird is actively positioning itself as a strictly sovereign European alternative to legacy SSL VPNs like Fortinet and Sophos. By keeping the control plane completely open-source, the platform allows IT administrators to self-host the entire infrastructure on their own hardware.
Why the Open-Source Mesh Network is Defeating Traditional VPNs
Traditional corporate VPNs force all traffic through a single central gateway. If that hardware fails, the entire remote workforce goes offline instantly. Mesh networks solve this single point of failure by allowing devices to discover and connect directly to each other. If one node drops, the rest of the network simply routes around it.
NetBird takes this concept further by competing head-to-head with proprietary, cloud-closed mesh networks like Tailscale and ZeroTier. Because NetBird is fully open-source, businesses and privacy-conscious users do not have to hand their metadata over to a third-party company in the United States. You keep complete sovereignty over your network routing.
This transparency is exactly why homelab enthusiasts are abandoning manual configurations. You get the enterprise-grade visibility of a commercial Zero Trust dashboard, coupled with the uncompromising privacy of running it on your own Linux server. The command line will always be there, but you finally stop needing it for basic network survival.